
Healthcare IT
Endpoint support, secure configuration, and connectivity troubleshooting in regulated environments.
Automation / IT support / Cybersecurity
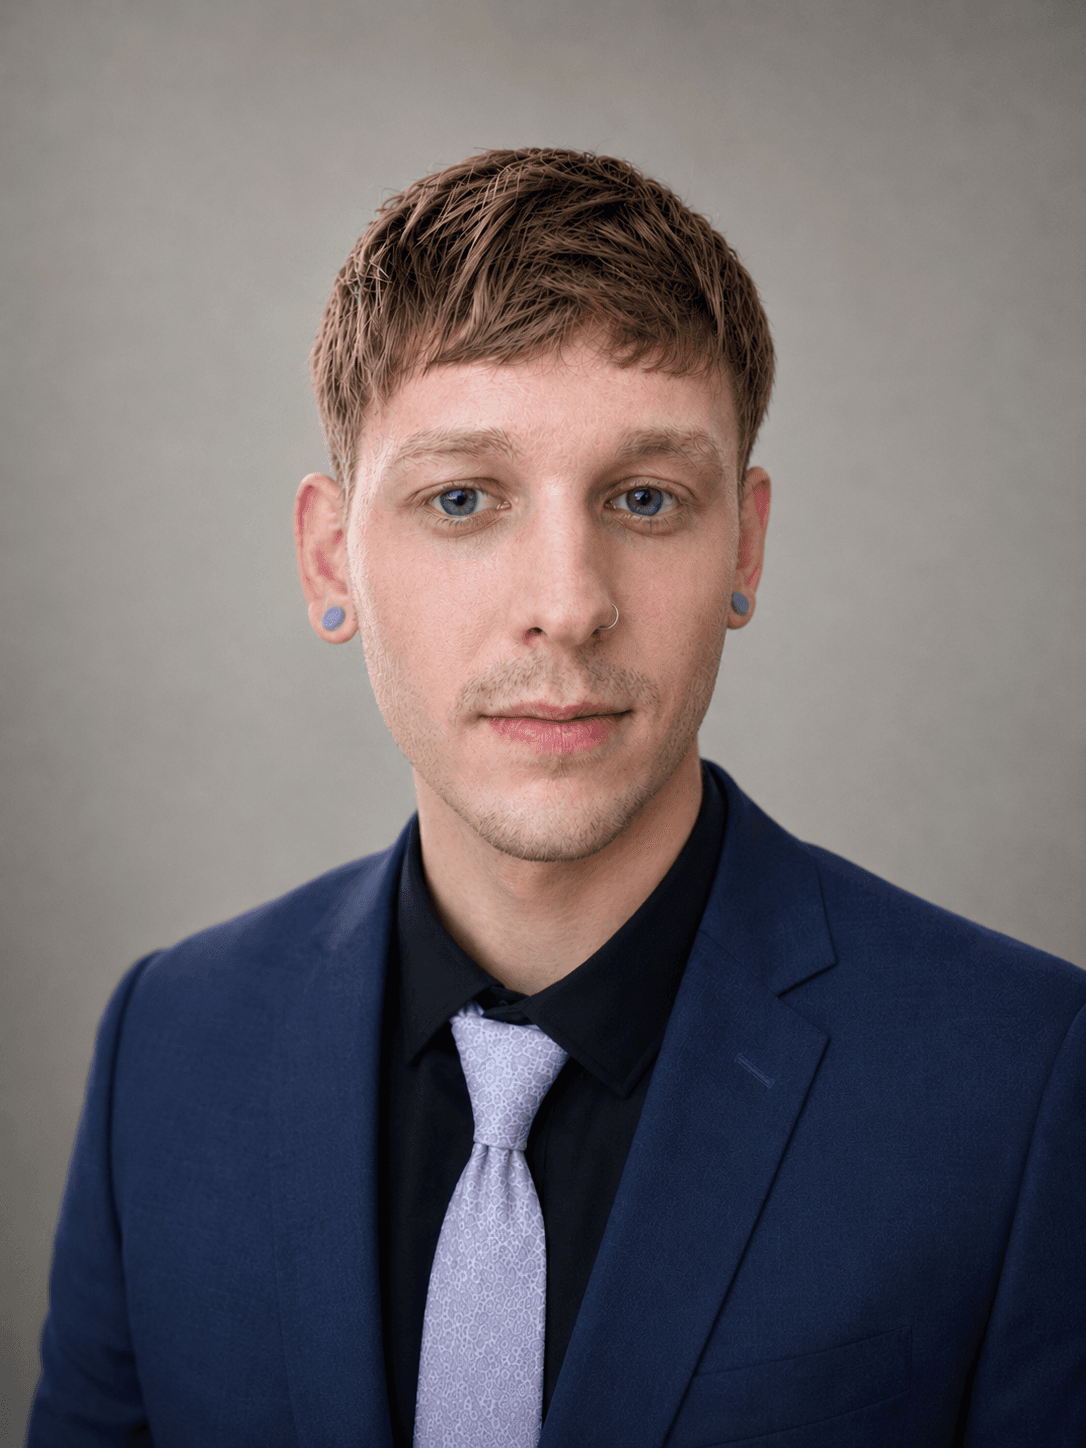
I’m Cameron Hecox. I help teams reduce repetitive work, solve everyday IT problems, and strengthen security. My experience in healthcare IT, detection engineering, and security operations informs practical automation, useful AI integration, and improvements people can maintain.
IT support
Workflow automation
Security operations
AI & workflow integration
Career at a glance
Endpoint support, secure configuration, and connectivity troubleshooting in regulated environments.
Lead SOC Analyst / Detection Engineer experience in a multi-tenant MSSP.
Reported reduction in false positives across targeted high-volume SIEM categories.
Python, PowerShell, Bash, SOAR workflow contributions, and local AI enrichment.
01 / Consulting services
Start with the problem you need to solve. Explore the scope, likely deliverables, and experience behind each service.
Connect systems, simplify handoffs, and automate repeatable work. Add AI where it makes information easier to use and decisions easier to support.
Explore this service 02 / IT support & secure foundationsResolve the immediate problem, understand what keeps causing it, and strengthen the systems your people rely on.
Explore this service 03 / Security gaps & architectureUse an attacker’s perspective to examine how weaknesses could connect, where controls may fall short, and what architectural changes would strengthen defenses.
Explore this service 04 / Detection & security operationsImprove detection quality, connect the evidence analysts need, and automate routine investigation steps while keeping judgment with the analyst.
Explore this serviceScripting, SOAR workflow contributions, and independent AI enrichment projects inform how I identify repetitive work and build useful improvements.
Healthcare IT support experience keeps the focus on users, endpoint reliability, connectivity, and secure configuration.
Vulnerability awareness and detection, security gap analysis, and architectural recommendations connect possible attack paths with practical defensive improvements.
Multi-tenant SOC work, detection tuning, complex escalations, and analyst mentoring bring an operational perspective to alerts and investigations.
Start a conversation